Russian-linked hackers tunneled into NATO shipbuilder’s network, Symantec says
A defence-sector campaign reached three organisations in two NATO countries; investigators have yet to establish whether sensitive information was stolen.
Russian-linked hackers stole credentials and opened a tunnel into a naval shipbuilder’s internal network during an espionage campaign that also targeted a military aircraft-engine maker and a law-enforcement agency, Symantec disclosed on October 20.
The security company attributed the activity to Swallowtail, also known as APT28 or Fancy Bear. It identified targets in two NATO member states. The Record, which interviewed a Symantec analyst, said the victims were European; their names and countries were withheld.
At the shipbuilder, the first confirmed infection followed the opening of a malicious Word attachment on July 24. Symantec’s account describes operators returning repeatedly during the following week, collecting credential material and mapping computers inside the organisation. A network tunnel gave them a route back through the compromised machine.
The attackers also deployed an undocumented loader that decrypted and executed a separate payload in memory. Investigators recovered the key and the encrypted file’s name, but the payload itself was missing. Its ultimate function remains unknown.
Traces appeared as late as September 24. That two-month span establishes the duration of observed activity; researchers could not establish uninterrupted access across the period. Symantec said later traces could reflect recurring tasks or renewed attention from the operators.
Dick O’Brien, a Symantec intelligence analyst, told The Record that researchers could not determine whether sensitive information had been stolen. He considered defence-related information a reasonable assumed objective given the victims, and said weeks on some networks could have created opportunities to obtain it.
The case leaves European defence suppliers facing a documented intrusion with an unresolved account of data loss. Symantec’s findings establish access, credential theft and new tooling; the assessment of the attackers’ collection objectives remains attributed to the researchers.
Attribution follows Symantec’s assessment. Neither source contains a Russian response.
Corrections & updates
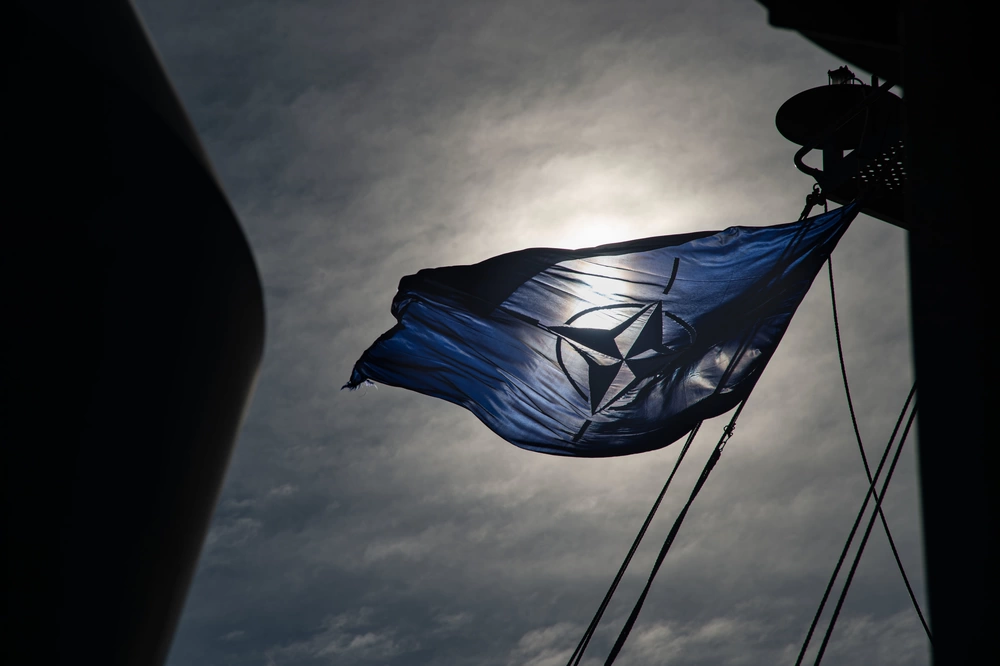
23 Oct 2026 Image delivery repaired using the identical U.S. Navy NATO-flag photograph from its original DVIDS record. The earlier media.defense.gov file refused requests. Photograph, archive caption, credit, article text and canonical URL are preserved.
Sources & further reading
- Swallowtail targets defense firms in two NATO countriesSymantec / Broadcom Threat Hunter Team
- Defense contractors in two NATO allies hacked in Russia-linked campaignThe Record
SPY REGISTER MEMBERSHIP
Stay on the case.
Follow this story through the case files, read The Brief and keep your own saved reports.
$6.67 a month equivalent · $80 billed annually. Or $8 monthly.
Get the member edition →Renews automatically. Cancel renewal online.