ESET Says Belarus-Linked Hackers Deployed Wiper at Ukrainian Transport Supplier
FrostyNeighbor moved from espionage tooling to a destructive script, according to ESET. The victim, damage and motive remain undisclosed.
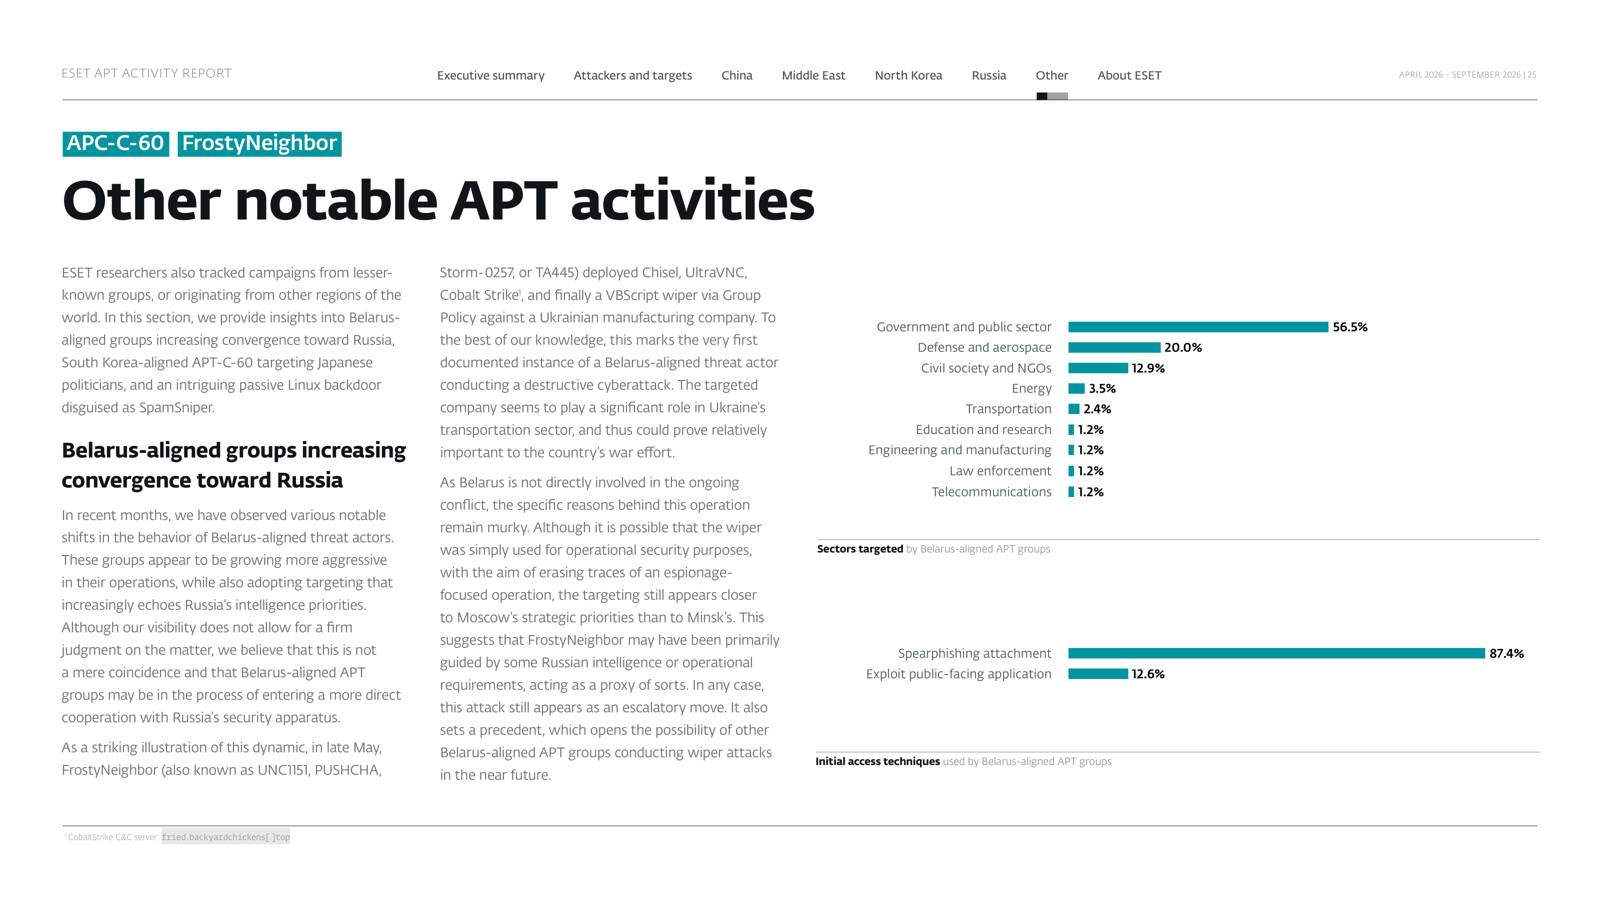
ESET says a Belarus-linked hacking group deployed a data-destroying script inside an unnamed Ukrainian manufacturer important to the country’s transport sector, marking the first destructive operation by such an actor that the company has documented.
The late-May intrusion began with tools built for access and control: Chisel, UltraVNC and Cobalt Strike. ESET’s report says FrostyNeighbor then pushed a VBScript wiper across the victim’s network through Group Policy, the Windows mechanism administrators use to impose settings across many machines.
ESET did not name the manufacturer, quantify the damage or publish victim confirmation. Its researchers said the wiper may have been used to erase traces left by an espionage operation. They called the reasons for the attack murky and stopped short of claiming that Minsk or Moscow ordered it.
The group is also tracked as UNC1151, Ghostwriter, PUSHCHA, Storm-0257 and TA445. In May, ESET documented a separate campaign against Ukrainian government organizations that used malicious PDF links, a JavaScript loader and Cobalt Strike after the operators screened potential victims.
Other researchers have independently tied the actor to Belarusian espionage, though not to this specific destructive attack. Mandiant assessed with high confidence in 2021 that UNC1151 was linked to the Belarusian government, while saying it had no direct evidence of Russian contributions. SentinelLABS later documented Ghostwriter campaigns against Ukrainian military and government targets and Belarusian opposition activists.
ESET argues that Belarus-aligned operations are increasingly echoing Russian intelligence priorities and may be moving toward a proxy role. Its report also says visibility is too limited for a firm judgment. Reform.news published a separate account of the finding but did not provide independent victim forensics or a response from Belarus.
The public evidence therefore establishes a named research finding, a documented tool chain and a longer espionage history. It does not establish who authorized the wiper, how much data was destroyed or whether the operation affected Ukraine’s transport system beyond the unnamed supplier.
The destructive incident is ESET’s research finding and has no public victim confirmation. The victim, damage and authorizing party are undisclosed. Independent research supports the actor’s historic Belarus link and Ukraine targeting, not this specific wiper event. No public Belarus response was located.
Sources & further reading
- ESET: FrostyNeighbor wiper and attribution limitsESET / original published reports
- Reform.news reports ESET Belarus-linked wiper findingsReform.news / original attributed reporting
- FrostyNeighbor: Fresh mischief and digital shenanigansESET / original technical research
- UNC1151 Assessed with High Confidence to have Links to BelarusGoogle Threat Intelligence / Mandiant original research
- Ghostwriter | New Campaign Targets Ukrainian Government and Belarusian OppositionSentinelLABS original threat research
SPY REGISTER MEMBERSHIP
Stay on the case.
Follow this story through the case files, read The Brief and keep your own saved reports.
$6.67 a month equivalent · $80 billed annually. Or $8 monthly.
Get the member edition →Renews automatically. Cancel renewal online.