Dream Says Hackers Reached U.S.-Linked Network Through Firewalls
An intrusion spanning four countries reached the credentials and internal directory of a government-affiliated environment, researchers report.
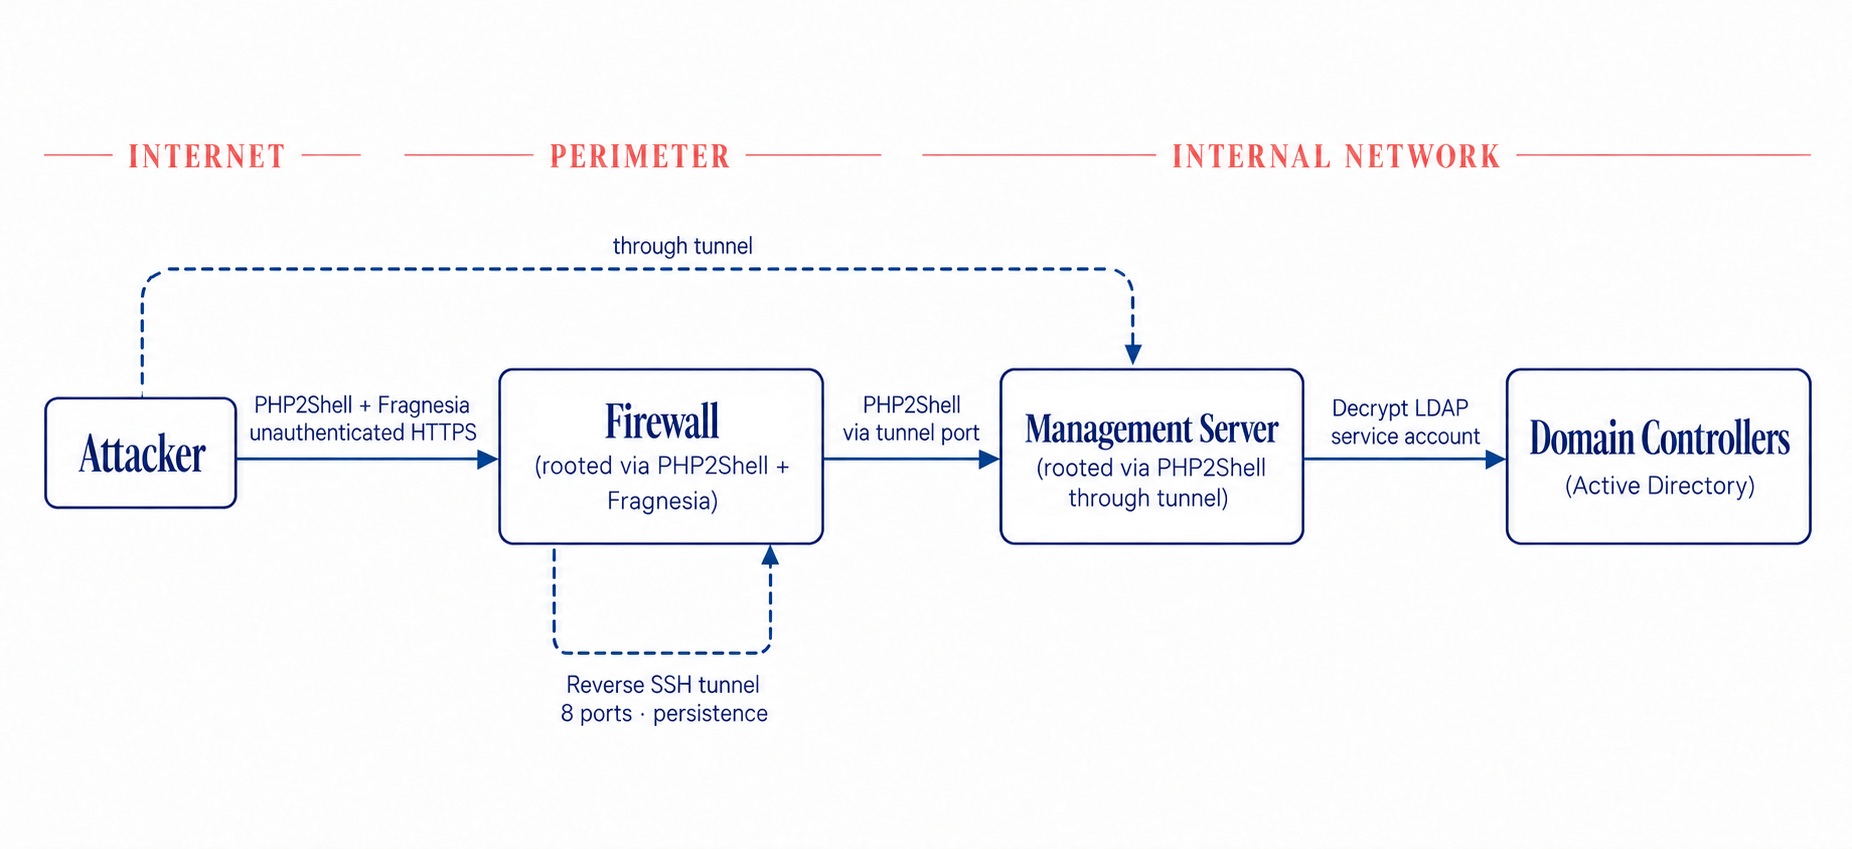
Attackers broke through perimeter firewalls and reached the internal login infrastructure of an unnamed U.S. government-affiliated organization, cybersecurity company Dream said in research published October 26.
From recovered artifacts, the researchers counted 24 compromised firewalls across the United States, Japan, Taiwan and South Korea, plus an internal management server.
Inside the U.S.-linked environment, a compromised firewall became a route to the server managing the organization’s other firewalls. Dream says the intruder recovered a service-account password and listed the network’s users and groups.
The researchers could not establish whether subsequent password attacks, attempts to create hidden accounts or efforts to steal sign-on keys succeeded. They withheld the firewall vendor and affected versions, saying the vendor had been notified.
Dream inferred the government connection from system configurations, including Common Access Card authentication. It did not name the organization. Security Boulevard reported the findings the following day.
Vendor report, not independently confirmed victim intrusion. Government affiliation inferred by Dream; organization and firewall vendor undisclosed. No named threat actor or definitive Chinese-state attribution asserted. Unknown outcomes of further password attacks and account creation preserved. No contact or victim confirmation by Spy Register. Full original primary turn625view0 and independent authored SecurityBoulevard turn626view0 read. Illustration conceptual, no event photography; generatedfile exec-2a22f3a7-439d-4f22-9aa4-205819c4f5ea.png full/mobile360/thumbnail160 actually viewed; exact production delivery200 PNG2519882bytes actually inspected and matching selected image.
Corrections & updates
28 Oct 2026 Removed the generic generated lead illustration following an image-quality review. A relevant documentary replacement has not yet been cleared.
28 Oct 2026 Replaced the removed illustration with Dream’s actual published attack-path diagram, identified as the company’s reconstruction.
Sources & further reading
- Dream: Chained PHP2Shell Exploit Roots 25 ServersDream / original technical research
- CISA Says PHP2Shell Flaw Under Attack as Reports of More Come InSecurity Boulevard / original reporting
SPY REGISTER MEMBERSHIP
Stay on the case.
Follow this story through the case files, read The Brief and keep your own saved reports.
$6.67 a month equivalent · $80 billed annually. Or $8 monthly.
Get the member edition →Renews automatically. Cancel renewal online.